Issue Description
Summary
On a fresh Stalwart v0.16.18 installation, outbound messages are signed with both the automatically generated RSA and Ed25519 DKIM signatures, but Gmail reports both signatures as failed.
The problem does not appear to be DNS publication, message mutation, SPF, source-IP selection, or body canonicalization.
Environment
- Stalwart: v0.16.18
- Operating system: Windows Server 2025 Standard
- Database: MySQL 8.4.11
- Blob storage: local filesystem
- Directory: internal
- Installation: fresh setup using the Stalwart WebUI wizard
- DKIM keys: automatically generated by Stalwart during setup
- Outbound delivery: direct to recipient MX, no SMTP relay
- Test recipient: Gmail
Domain and selectors
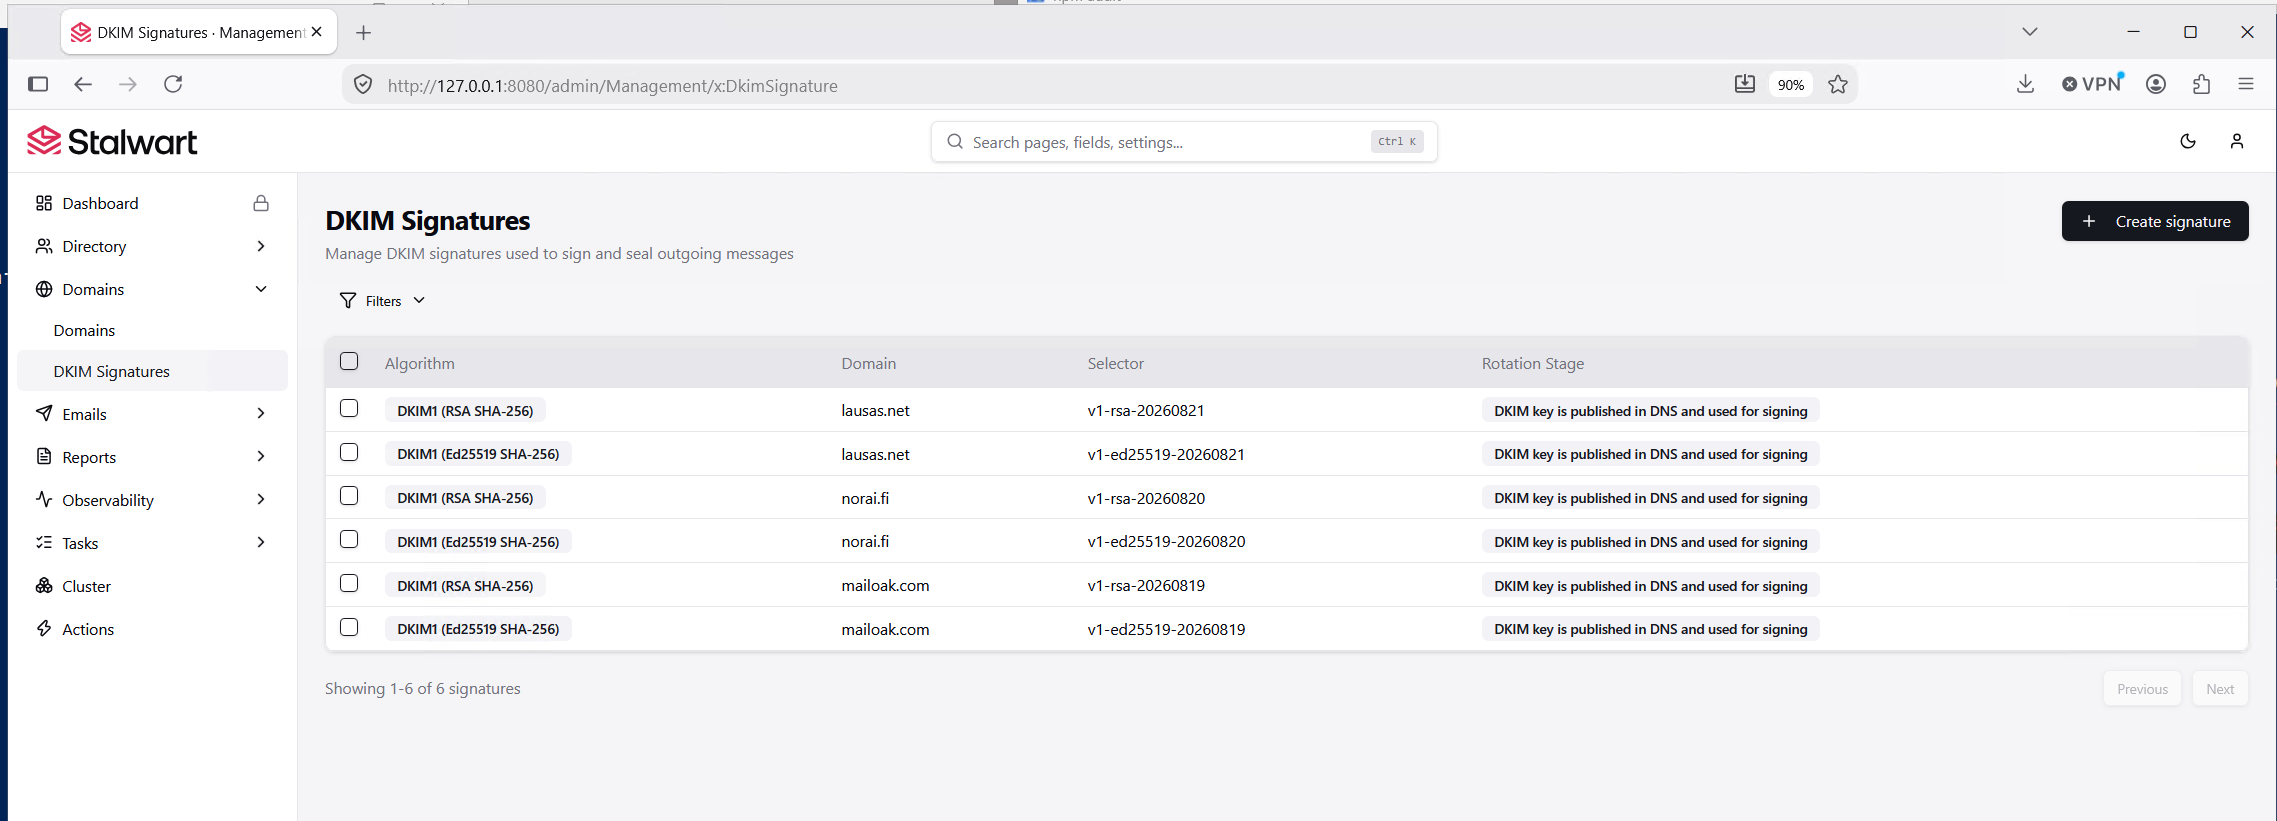
Domain:
mailoak.com
Selectors:
v1-ed25519-20260819
v1-rsa-20260819
The Ed25519 public key shown by Stalwart under the DKIM signature object is:
SJuRaRsbyGkh4lKo//AA5zRjMWcIVpcYm/nkNN2/Dk4=
The public DNS record contains the exact same key:
v=DKIM1; k=ed25519; h=sha256; p=SJuRaRsbyGkh4lKo//AA5zRjMWcIVpcYm/nkNN2/Dk4=
The RSA public key shown/generated by Stalwart was likewise published directly in DNS.
Both records resolve publicly from Google and Cloudflare DNS.
Reproduction
- Install Stalwart v0.16.18 on Windows Server 2025.
- Configure a local domain through the setup wizard.
- Enable automatic DKIM key generation.
- Publish the generated RSA and Ed25519 public keys in DNS.
- Create a normal user account.
- Submit a message through Stalwart’s authenticated SMTPS listener on port 465.
- Allow Stalwart to deliver directly to Gmail.
- Inspect Gmail’s “Show original” output.
Expected result
At least the RSA DKIM signature, and ideally both signatures, should verify successfully.
Actual result
Gmail reports:
dkim=fail [email protected] header.s=v1-ed25519-20260819
dkim=fail [email protected] header.s=v1-rsa-20260819
spf=pass
dmarc=pass
SPF passes using the intended dedicated sending IP:
51.83.169.75
DMARC passes through aligned SPF.
Relevant received headers
Authentication-Results: mx.google.com;
       dkim=fail [email protected] header.s=v1-ed25519-20260819;
       dkim=fail [email protected] header.s=v1-rsa-20260819;
       spf=pass (google.com: domain of [email protected] designates 51.83.169.75 as permitted sender) [email protected];
       dmarc=pass (p=NONE sp=NONE dis=NONE) header.from=mailoak.com
The message was received directly from the intended Stalwart host:
Received: from smtp.mailoak.com (smtp.mailoak.com. [51.83.169.75])
        by mx.google.com with ESMTPS
        (version=TLS1_3 cipher=TLS_AES_256_GCM_SHA384 bits=256/256)
Stalwart emitted both signatures:
DKIM-Signature: v=1; a=ed25519-sha256;
 s=v1-ed25519-20260819;
 d=mailoak.com;
 c=relaxed/relaxed;
 h=Subject:Message-ID:Date:To:From;
 bh=ymp4mDy0dOH0P1M4+xU9vVowuXejoGXdc3J+b5JDfYM=;
 ...

DKIM-Signature: v=1; a=rsa-sha256;
 s=v1-rsa-20260819;
 d=mailoak.com;
 c=relaxed/relaxed;
 h=Subject:Message-ID:Date:To:From;
 bh=ymp4mDy0dOH0P1M4+xU9vVowuXejoGXdc3J+b5JDfYM=;
 ...
Verification already performed
Body hash
The received message body was independently canonicalized using relaxed DKIM body canonicalization and SHA-256.
The calculated body hash is:
ymp4mDy0dOH0P1M4+xU9vVowuXejoGXdc3J+b5JDfYM=
This exactly matches the bh= value in both Stalwart-generated DKIM signatures.
This appears to rule out message-body mutation after signing.
Public key
For the Ed25519 signer, the public key shown by Stalwart as derived from the stored private key is byte-for-byte identical to the public key published in DNS:
SJuRaRsbyGkh4lKo//AA5zRjMWcIVpcYm/nkNN2/Dk4=
Therefore this does not appear to be the public/private key mismatch described in issue #3188.
Independent signature verification
The Ed25519 b= signature from the Gmail-received message was independently verified against that exact public key and did not validate.
The same verifier was first tested against the RFC 8463 Ed25519 DKIM test vector, which validated correctly.
Other mail-path checks
- Forward DNS is correct.
- PTR matches
smtp.mailoak.com. - SPF passes.
- Outbound source IP is explicitly bound to
51.83.169.75. - TLS works correctly.
- Gmail receives the message directly from the expected IP.
- No intermediary SMTP relay is involved.
- DMARC passes via SPF alignment.
Related issues
This appears related to, but distinct from:
- #3193 - Ed25519 DKIM fails while RSA passes.
- #3188 - RSA private/public key mismatch after a setup-wizard race.
In this case:
- both RSA and Ed25519 fail
- the Ed25519 public key derived by Stalwart matches DNS exactly
- the DKIM body hash matches the received body
- the setup completed successfully
- there is no third-party relay modifying the message
Additional evidence
A raw Gmail .eml containing both DKIM signatures and Gmail’s Authentication-Results is available if useful.
Happy to run a more targeted trace or provide canonicalized header bytes if maintainers need them for reproduction.
Stalwart Version
v0.16.x
Installation Method
Binary (Windows)
Database Backend
MySQL
Blob Storage
Filesystem
Search Engine
MySQL
Directory Backend
Internal
Additional Context
wrapped the executable with NSSM as the Windows service
I have reviewed the documentation and FAQ and confirm that my issue is NOT addressed there.
on
I have searched this support forum (open and closed topics) and confirm this is not a duplicate.
on