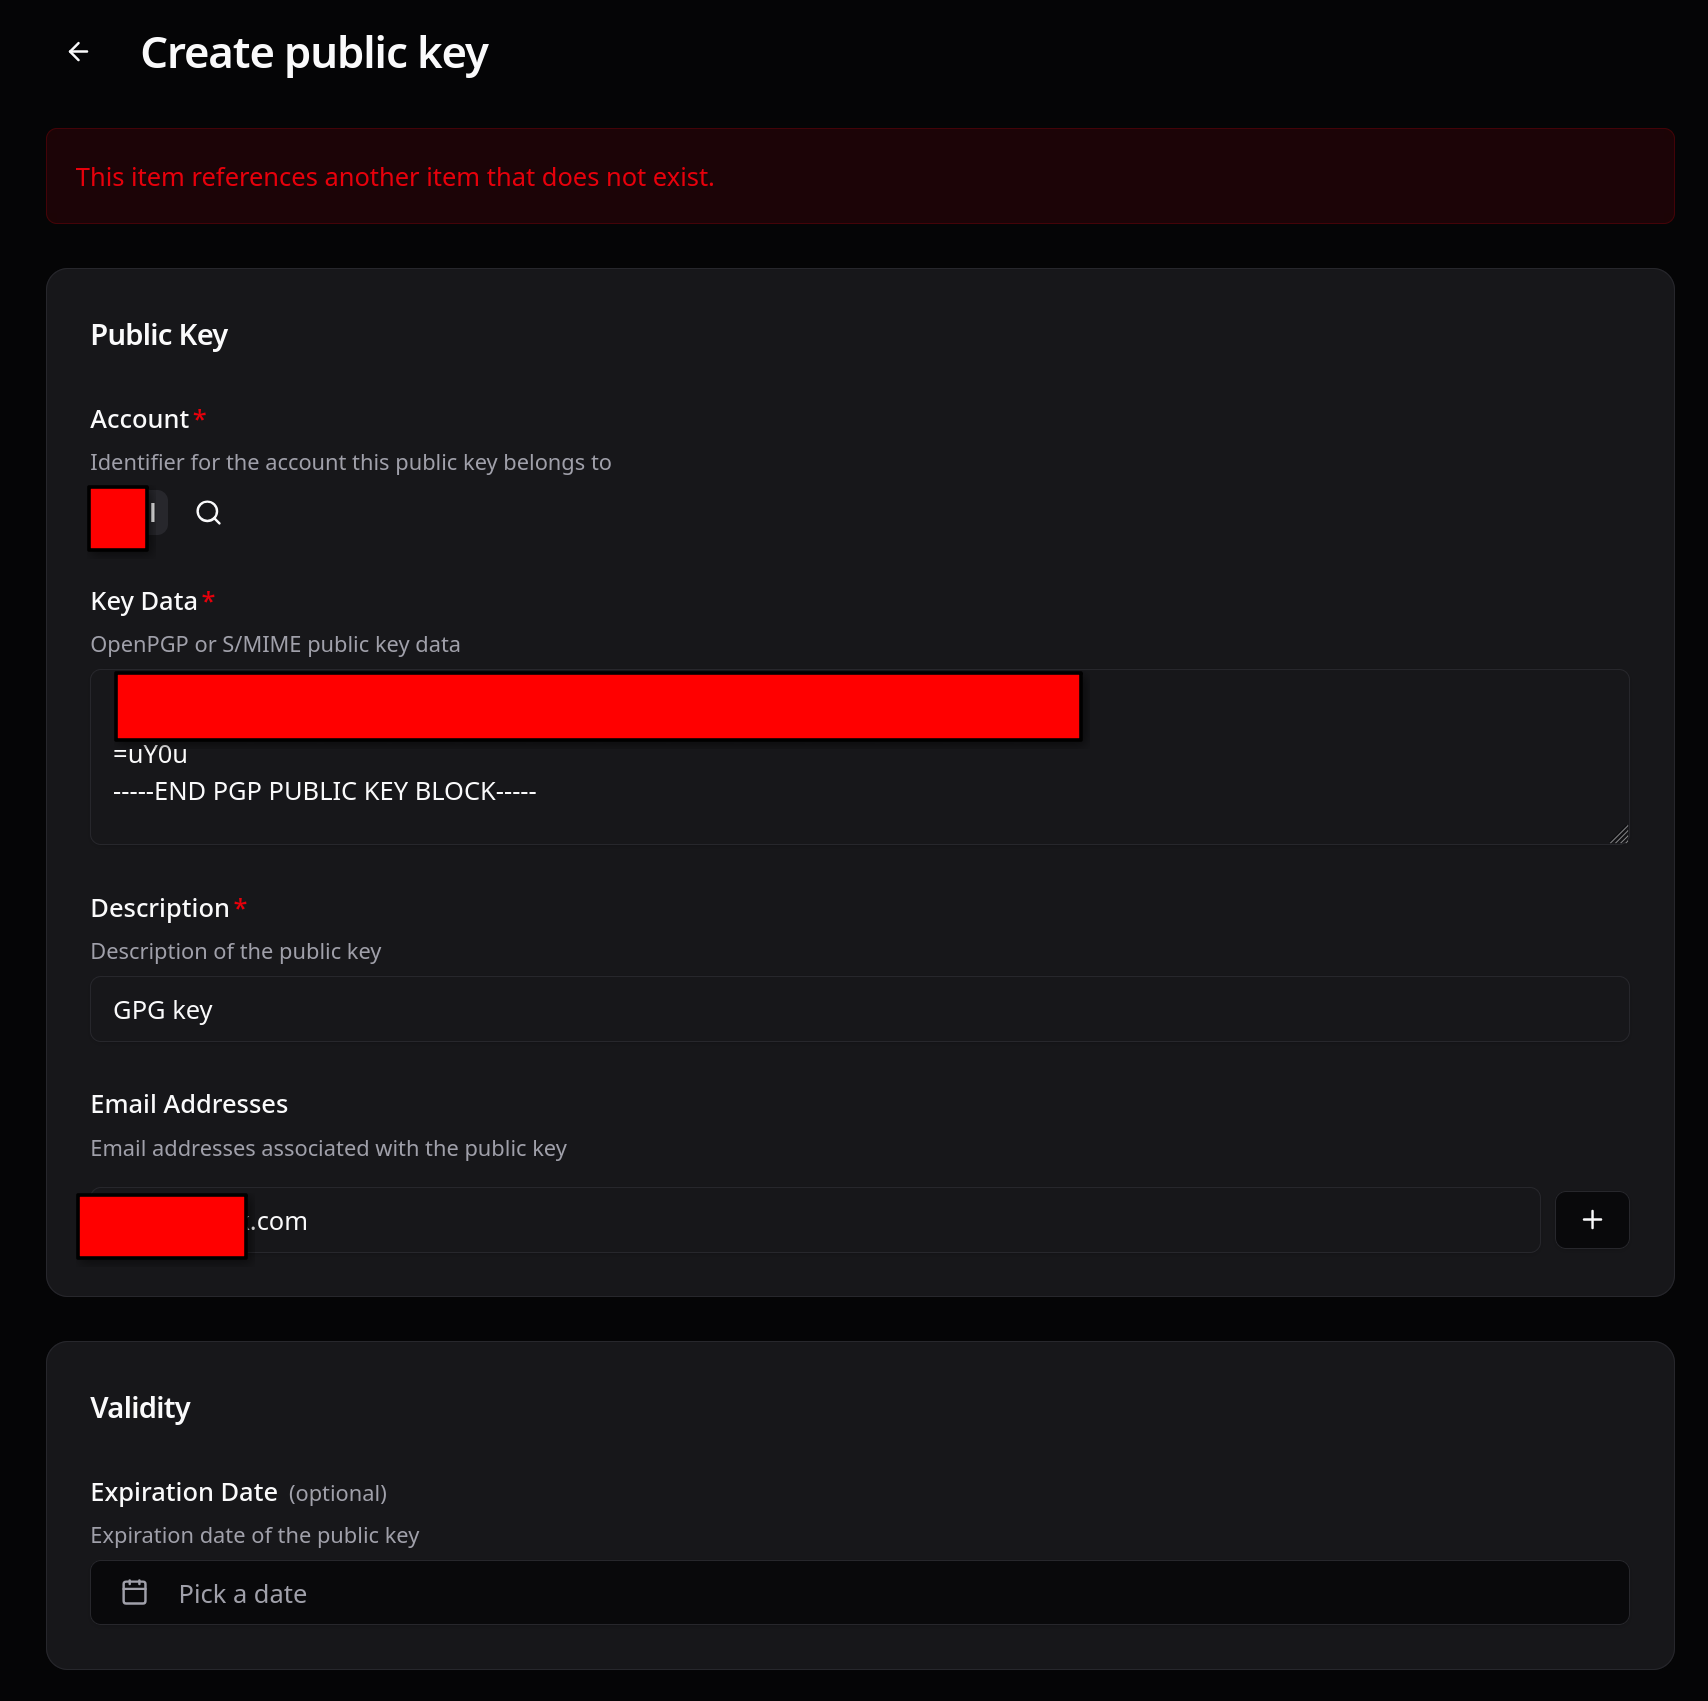
Your question
This item references another item that does not exist.
The error “This item references another item that does not exist” means the encryptionAtRest field on the user’s AccountSettings singleton is pointing to a PublicKey id that no longer exists (or was never successfully created).
Encryption at rest works in two steps:
PublicKey object must be registered first (containing the OpenPGP key or S/MIME certificate).AccountSettings singleton’s encryptionAtRest field references that key by id.If step 1 was skipped, failed, or the key was later deleted, you will get exactly this kind of “references another item that does not exist” error when trying to activate or update encryption. The fix is to:
/crypto endpoint) or via the JMAP API as a PublicKey object.encryptionAtRest on the account, referencing the id of the key you just registered.If you are working via the WebUI’s account manager, make sure the key upload step completed successfully before clicking to enable encryption.
More details are in the Encryption at Rest - Management documentation page.
This is an automated reply from the Stalwart Help Bot. Other community members may follow up if this answer is incomplete or wrong.
i tried it several times with the web ui, but it doesn’t work.
how is the correct syntax for doing this with stalwart-cli?
The Error ist quite persistent. Even deleting and recreating of the account didn’t make the error go away.
Please Help!
“This item references another item that does not exist.”
A shot in the dark but you could try going to Actions and clearing the caches.
thanks for your proposal, but this didn’t solve it.
That message is a foreign-key error: the encryption-at-rest setting is pointing at a public key that does not exist for that account, which is also why clearing the caches did not change anything. The order matters here: you need to register a public key (an OpenPGP key or an S/MIME certificate) for the account first, and then enable encryption at rest referencing that key.
The flow is documented at Management | Stalwart. If you already created a key, double-check the key id you are referencing still exists.
Try to properly export the public key. I had the same issue due to a corrupted public key export.
If i create a user with ‘Administrator Role’ i am able to create a Public Key. However if a user has ‘User Role’ i get that error message.
I am wondering if this is a permission issue. Is there any specific permission which a ‘User Role’ needs to have to create Public Key?
@trumee that error means the accountId on the create did not resolve, so it is about the account reference rather than the key material or anything wrong with the key itself.
The role explanation does not quite hold up, which is why I want more detail before guessing. On a stock install the User role already carries the public-key permissions (they are in the default user and group permission sets, not just the superuser one), and a missing permission would come back as a forbidden error rather than an invalid foreign key. So either the roles in your install have been customised, or the two cases differ in which account is actually being referenced.
Could you post the create request payload and the JSON error response from the browser network tab, and say whether you are signed in as an admin creating the key for a User-role account or signed in as that user? Also useful: the effective permission list on the failing account (specifically whether sysPublicKeyGet and sysPublicKeyCreate are there), your version, and whether this install was migrated from an earlier 0.16.x. Separately, is the “no key field at all” you mentioned the same accounts, or a different symptom?
After setting the Roles in account/Management/x:Role the problem went away.