Your question
Hi Stalwart Support Team,
I currently have an existing ENTERPRISE Stalwart server running an older version, where outbound DKIM signing works properly.
Recently, I set up a new virtual machine running the latest version of Stalwart and replicated all configurations from the existing server—including using the exact same private key.
However, during testing, the email header analyzer mxtoolbox reported the following error:
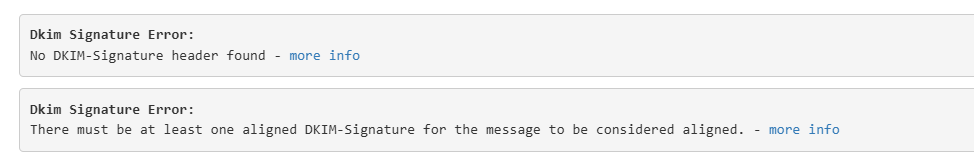
"Dkim Signature Error:
No DKIM-Signature header found - more info
Dkim Signature Error:
There must be at least one aligned DKIM-Signature for the message to be considered aligned. - more info"
“No DKIM-Signature header found” (There must be at least one aligned DKIM-Signature for the message to be considered aligned).
Even though the configuration and private key match the working older instance, the outgoing messages are not being signed. Could you please guide me on which configuration parameters or breaking changes in the latest version I need to check or adjust to resolve this issue?
Thank you for your assistance.
I understand that topics in this category are triaged by a bot first but a human reply will follow up. If I’d prefer a human-only reply, I’ll add the no-ai tag to my topic.
on
Hello @mdecimus can you assist me for my problem ?
The default signing policy changed between 0.15 and 0.16, and that is where I would look first. 0.15 signed anything that did not arrive on the port-25 listener. 0.16’s dkimSignDomain on the SenderAuth singleton defaults to is_local_domain(sender_domain) && !is_empty(authenticated_as), so an unauthenticated submission is not signed at all now. How was the test message submitted?
If it was authenticated, the next suspect is the binding. In 0.16 a DkimSignature points at a Domain object through domainId, where 0.15 carried a plain domain string. If that points at the wrong Domain, or the sender domain has no Domain object at all, no signer is found.
The log separates those two cleanly. A dkim.signer-not-found warning means the expression picked a domain but no usable signature was found, so a bad domainId, a stage that is not active, or a key that failed to parse. No such warning means the expression returned false and signing was never attempted in the first place.
One more thing to confirm: that the signature object is a Dkim1RsaSha256 or Dkim1Ed25519Sha256 variant. The DKIM2 variants emit a DKIM2-Signature header, which is exactly what mxtoolbox would report as a missing DKIM-Signature.