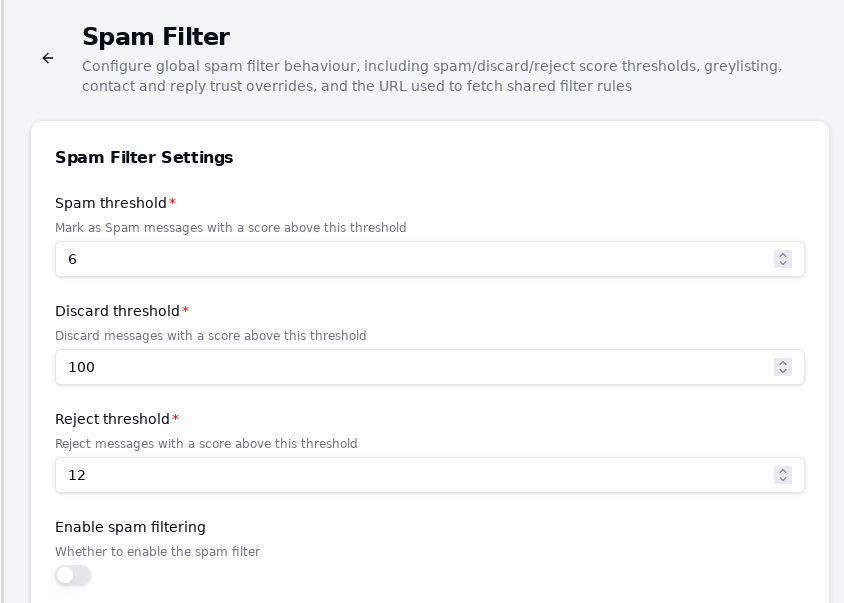
How to I correctly configure the Stalwart spam filter, if it operates behind an outer incoming Postfix MX server with spamassasin?
I have already tried to tell Stalwart that there is an upstead server in the Stalwart settings, but apparently to no avail.
The spam filter is entirely random. My Spam folder is full of ham. I received over 20000 mails in over 3 months, so plenty of training data, but the Spam folder contains about 50% are ham, which is the definition of random.
To avoid more problems, I put the reject threshold at 100 (!) (instead of 7), and people still get “Non-delivery” bounces that blame their mail server’s reputation. It’s like the spam filter is randomly assigning spam scores.
I suspect that Stalwart’s spam filter primarily looks at the previous hop mail server and how much spam it got from that server. If it doesn’t know that the previous hop is my own server, then it will blame my own incoming server as the spam origin and wildly attribute all my mail as spam just for coming from that server.
In theory, Stalwart could learn that 100% of all its incoming mail is from that server, but I guess it’s not that smart. And I haven’t found the settings knob to tell it that this server is the actual MX.
I understand that topics in this category are triaged by a bot first but a human reply will follow up. If I’d prefer a human-only reply, I’ll add the no-ai tag to my topic.
The fix is to configure Postfix to speak the Proxy Protocol to Stalwart (Postfix supports emitting it via upstream_proxy_protocol = haproxy on the smtp(d) service that relays to Stalwart), and add Postfix’s IP to Stalwart’s trusted proxy networks. Just telling Stalwart “there’s an upstream server” via a trusted-networks entry without the corresponding protocol on the wire won’t work, since Stalwart still needs an actual signal (a Proxy Protocol header) carrying the real client IP, not merely permission to trust the connecting address.
Without this, the spam filter (and SPF/DMARC) evaluate every message as if it came from Postfix’s own IP, which explains erratic scoring and false “sender reputation” bounces blamed on the wrong host: Stalwart is scoring Postfix’s reputation, not the real sender’s, and that score is essentially meaningless/random from the recipient’s point of view.
Steps:
On Postfix, enable Proxy Protocol on the SMTP client connecting to Stalwart (or, if going through an intermediate TCP proxy, configure that layer instead).
On Stalwart, set proxyTrustedNetworks on SystemSettings (Network › General in the WebUI) to include Postfix’s IP/CIDR, or set overrideProxyTrustedNetworks on the specific smtpNetworkListener.
Confirm with a test message that headers/logs show the real client IP, not Postfix’s, before trusting the spam score again. Consider reverting your scoreReject threshold back down to something sane (e.g. 7) once real IPs are flowing through, since 100 defeats the purpose of the filter entirely.
No, the fix should be entirely in Stalwart. Postfix is innocent here. Stalwart needs to learn what an MX is. And not assume that it’s the MX, “or else I will destroy your mail!”
Plus, the setting should be a single text field for the hostname, and should ideally already be part of the initial Stalwart setup dialog sequence.
This is a very very common case. Almost nobody will put their production mail server aside and start 100% Stalwart as their main mail server, directly on the internet, as only MX. There will always be at least a testing period where Stalwart gets a copy of the incoming mail. This setup should be obvious and simple, not difficult to find, and should not require upstream changes in the other mail servers.
The spam filter has no IP reputation scoring in it at all, so that is not what is happening. What breaks behind a relay is authentication: SPF is evaluated against the IP that connected, which is your Postfix, so it fails for almost every sender and the DMARC verdict follows it down.
The knobs are expressions on the SenderAuth object and they all have remote_ip in scope: set spfEhloVerify, spfFromVerify, dmarcVerify and reverseIpVerify to disable when remote_ip is your upstream MX. Leave dkimVerify alone, since DKIM signatures survive relaying intact and are the one authentication result still worth trusting in your setup. If you would rather skip filtering entirely for relayed mail, MtaStageData.enableSpamFilter takes the same variables.
What does the verbatim NDR text say? With your reject threshold at 100 the spam score path is unreachable, and DMARC only rejects when dmarcVerify is set to strict, which is not the default. Our own reject line reads “550 5.7.1 Message rejected due to excessive spam score.” If yours does not look like that, the bounces are coming from the Postfix in front.
Either way, three months of training behind the relay has taught the classifier a skewed picture of what authenticated mail looks like, so once the verify expressions are right the model will want resetting and retraining.
[email protected] (expanded from [email protected]): host
mail.example.com[11.22.23.45] said: 550 5.7.1 Message rejected due to
excessive spam score. (in reply to end of DATA command)
whereas mail.example.com is the Stalwart server. That’s what people sending me mail are getting.
Sorry. To be easy to use, Stalwart should have a single setting for the upstream MX server IP address, and it sets all those values accordingly. Also because Stalwart might gain features or have code changes in the future that are also affected by an upstream MX, so it makes sense to have a general setting for this.
This problem is so common that the question should be part of the standard setup sequence, not just somewhere in the settings. I think most (>50%) serious setups that try out Stalwart will have it running either in parallel to the production system during testing, and/or behind an existing MX. Very very people will try out Stalwart and immediately make it their only mail server, and drop Postfix, spam filter, existing mail store, all of them gone immediately at the very first test. That’s very unlikely. So, almost every person trying Stalwart will need this.
@Disrupt is correct, and the bounce you posted is the proof. That exact string comes from one place in our code, and that code cannot execute when the spam filter is disabled. So at the moment those messages were rejected, your change had not reached the running server. Settings are compiled into a snapshot when the server starts; saving in the UI writes the object and stops there. Actions, Reload, Server settings rebuilds it, as does a restart.
The same is true of the sender authentication expressions I gave you earlier: if you made those changes and saw no difference, they are sitting in the registry unapplied too.
After you reload, one more thing can reject regardless of your threshold: a tag whose score is the literal word reject short-circuits before the threshold is ever compared. One shipped tag does that, BLOCKED_DOMAIN, so if rejections continue with a threshold of 100, look at your blocked-domains list.
On the feature: no, there is nothing today that lets you say “this address is my upstream MX” and have the sender authentication checks, the filter and the throttles adjust together.